Your Compliance Department Stops Operating In Silos
BSA, fraud, KYC, payments, and vendor risk all visible under one deployment, your CCO stops chasing status across six separate functions.
AI For Financial Services Operations
Every compliance function runs on its own deadline. Missing one is enough. Keep your BSA team filing on time, fraud cases closing the week they open, and onboarding clearing before the next batch lands, one standard behind all of them.
“Working with you guys has been amazing. We don't have to guess as much what customers are searching for because we have an AI piece to it as well.”
BSA, fraud, KYC, payments, and vendor risk all visible under one deployment, your CCO stops chasing status across six separate functions.
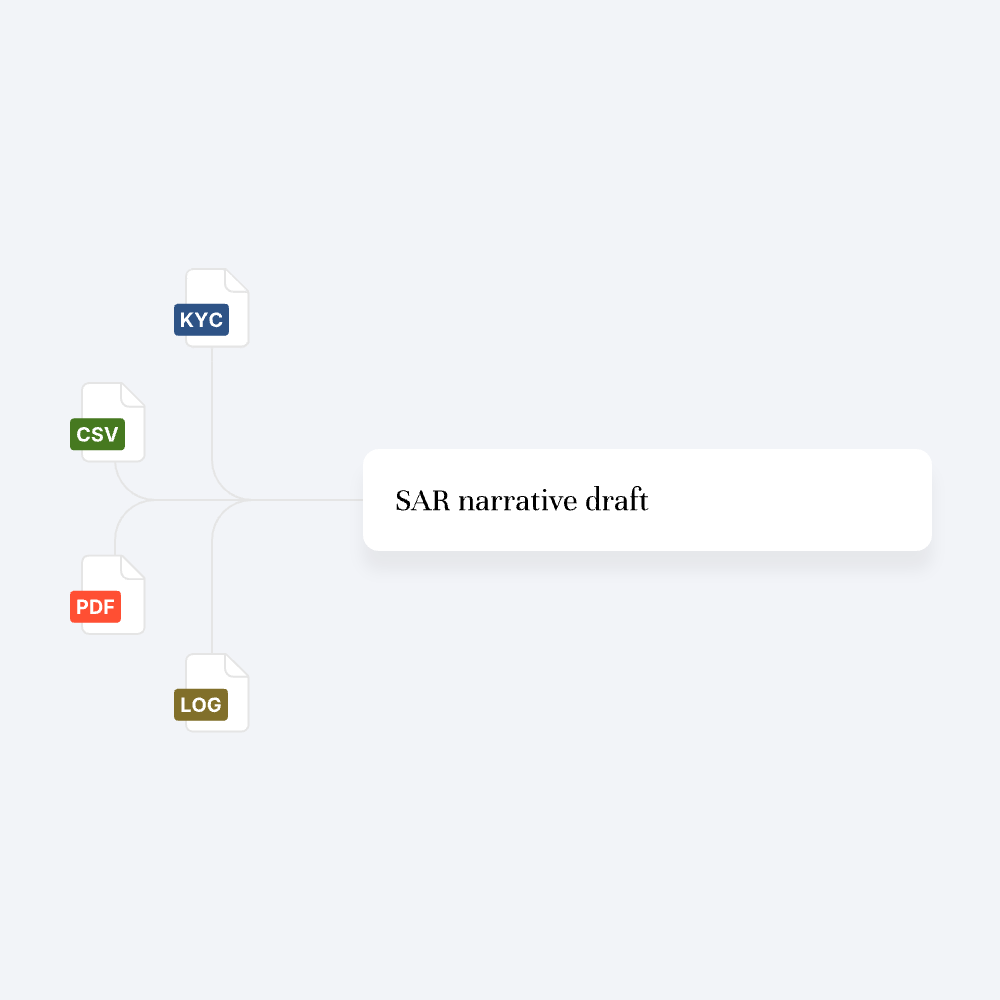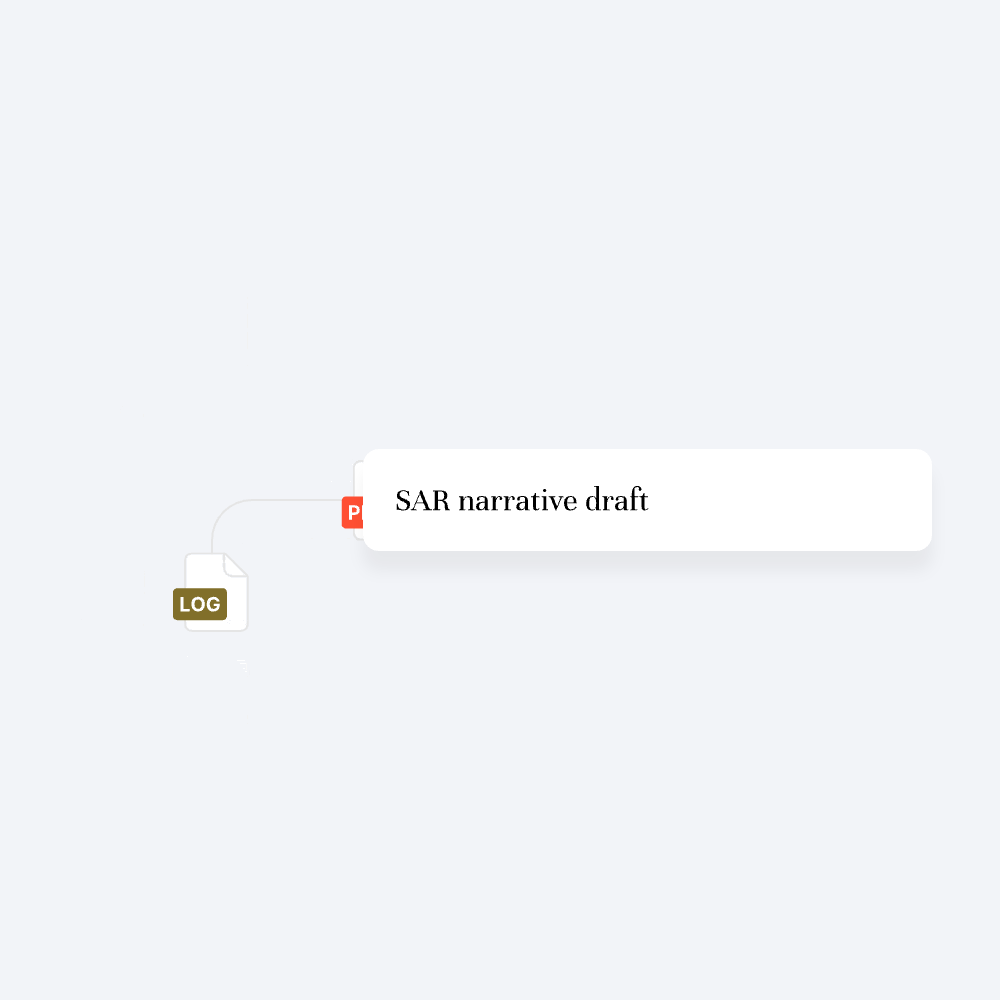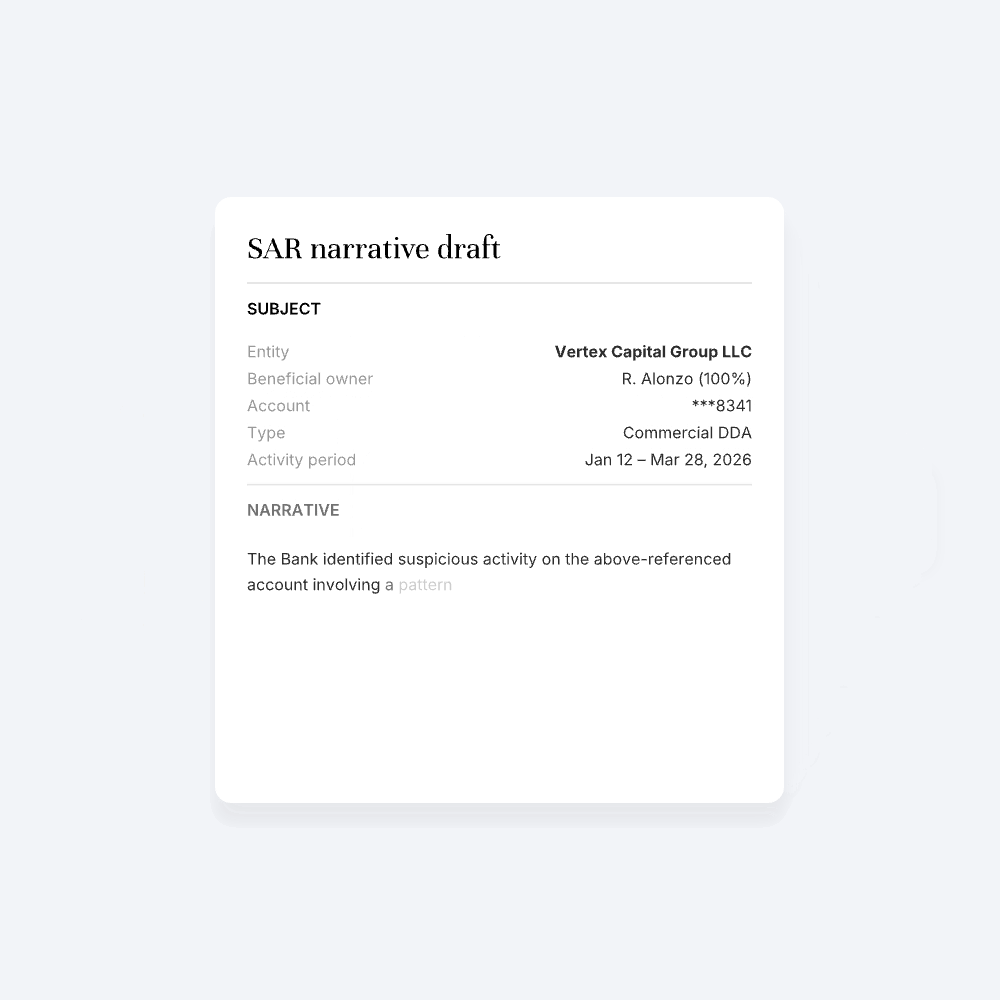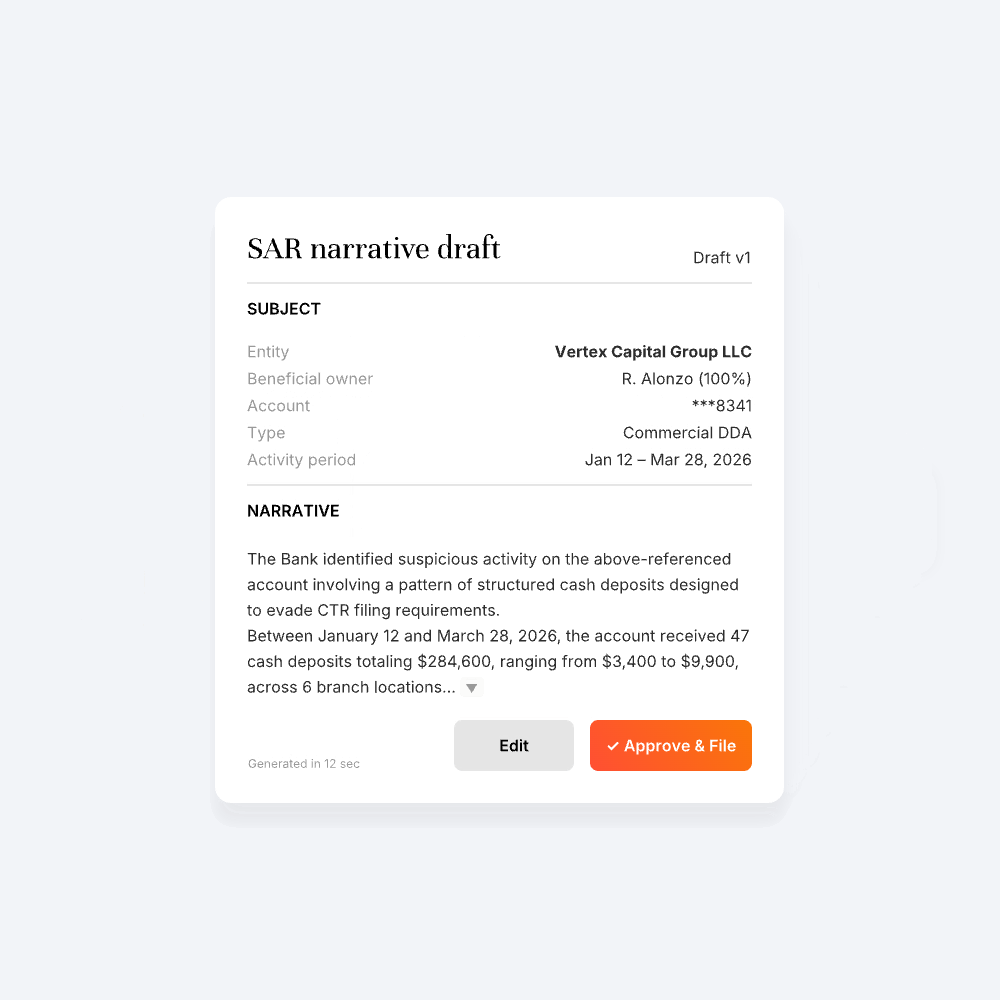
EDD assessments, SAR narratives, fraud dispositions, and vendor risk tiers all produced under the same documentation standard with every file consistent, sourced, and complete.
BSA officers review instead of drafting from scratch, fraud investigators start with a structured file, and KYC analysts clear onboarding queues without backlog.
Your compliance department runs six functions simultaneously, each with its own regulatory requirements, deadlines, and documentation standards. One deployment handles all of them without exception.

Screen incoming and outgoing ACH and wire transfers against OFAC lists, internal watchlists, and transaction limits. Flag anomalies, validate beneficiary details, and generate audit-ready logs.

Extract entity data from formation documents, verify beneficial ownership, run KYB screening, and produce a complete account opening package with risk classification and compliance sign-off.
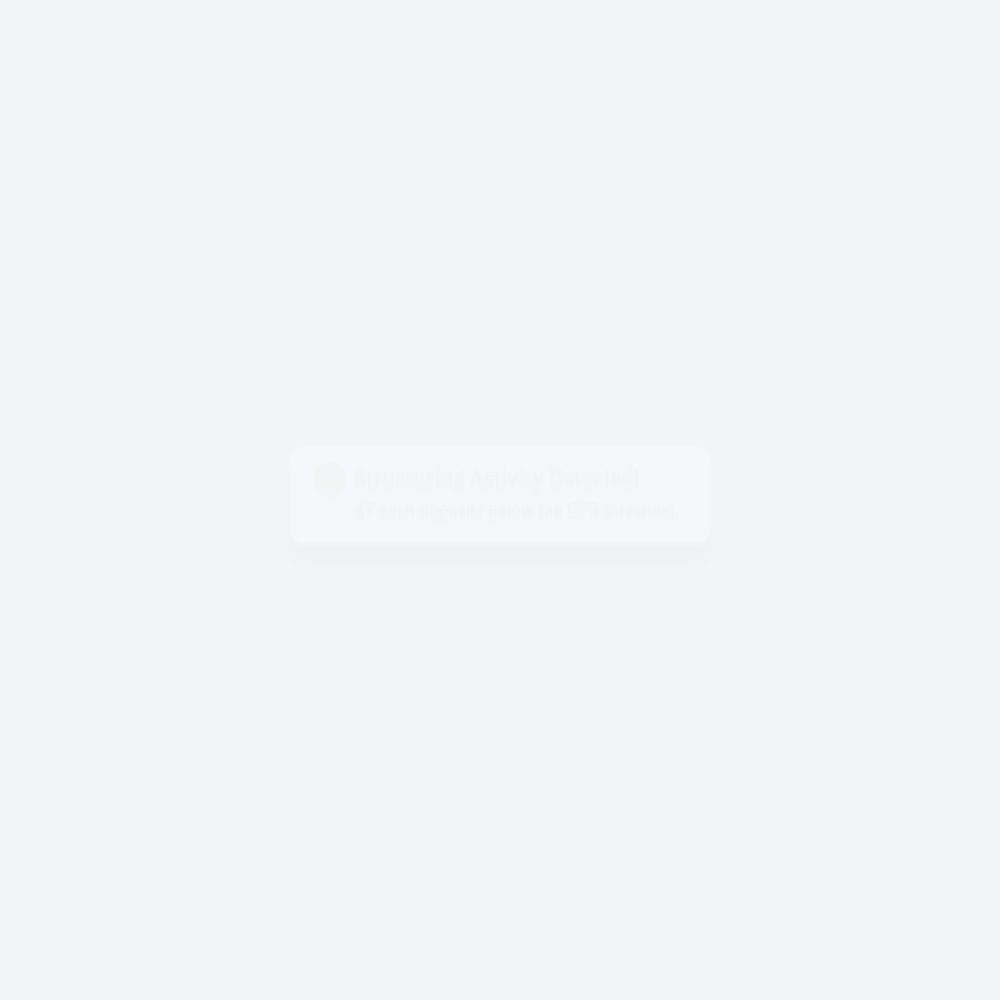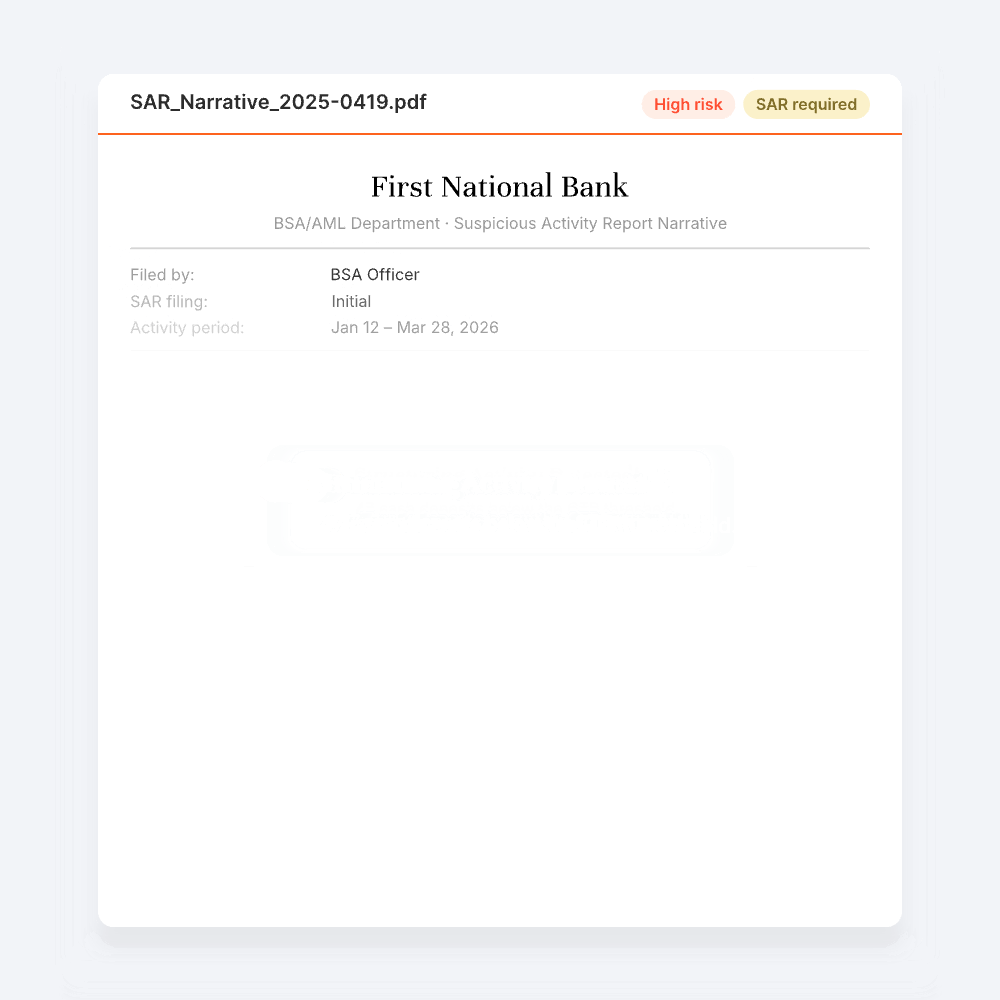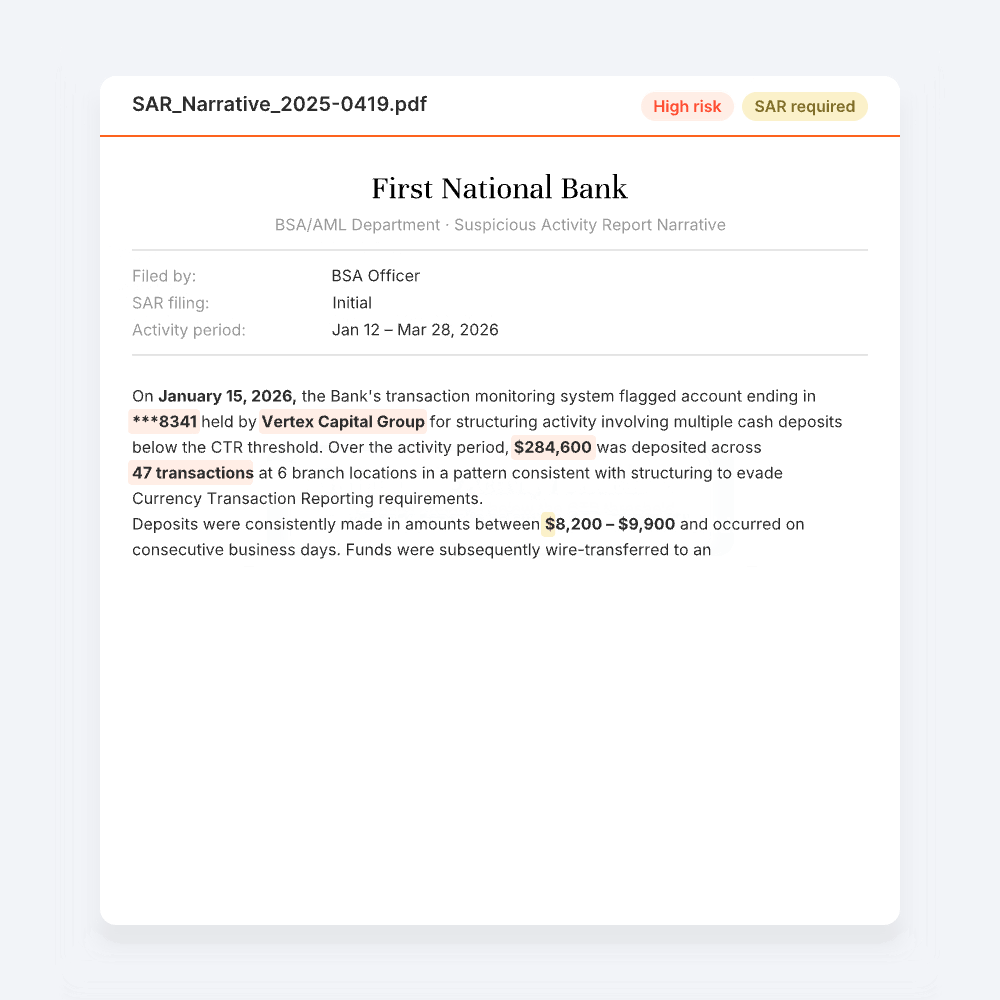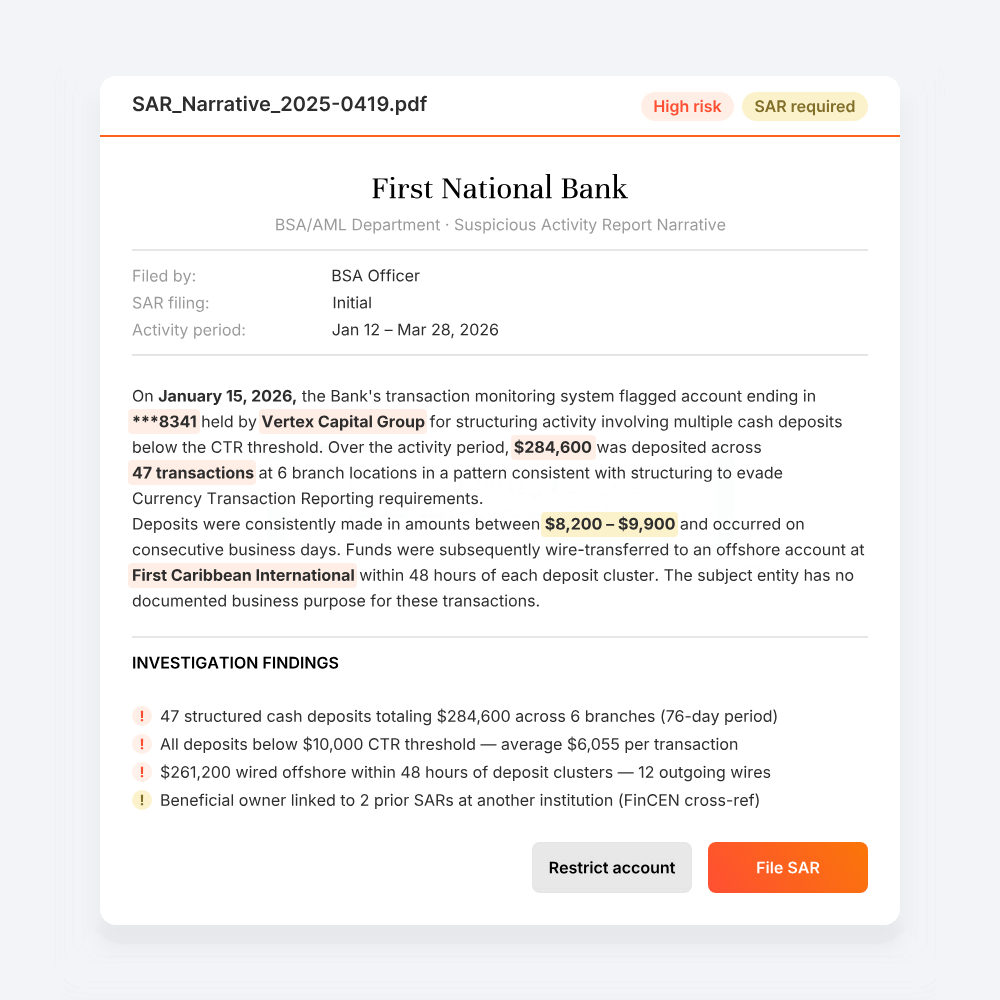
Consolidate transaction data, communications, and dispute records into a single investigation file. Build event timelines, cross-reference accounts, and generate findings reports for resolution.
Borrower data extracted, TRID timelines confirmed, and HMDA fields validated, the mortgage lending automation your compliance team needs, built into every residential file
BSA Officers
Compliance Analysts
Fraud Investigators
Payments and Deposit Operations
Vendor Risk Managers
Chief Compliance Officers


BSA/AM
FinCEN
Reg E
Reg CC
OCC
FDIC
NCUA
Bring one real case type (BSA/AML, fraud, onboarding, or payments). We’ll generate the evidence pack, disposition, and audit trail so your team can review the file on the spot.
Book A Proof-of-ConceptYes. Pre-built compliance automation workflows cover 24 case types across BSA/AML, account onboarding, deposit operations, fraud and risk, payments, and third-party risk management.
Yes. KYC processes, risk tiers, SAR thresholds, CTR triggers, EDD criteria, and vendor risk classifications all configured to your compliance policies.
Continuous monitoring workflows track activity patterns, flag threshold breaches, and update risk assessments automatically, your compliance analysts review exceptions, not raw data.
Yes. Encryption in transit and at rest, role-based access, and no model training on customer documents unless agreed in writing, customer PII and transaction data stay governed by your policies throughout.
Human review is built into every workflow. Analysts override any output, overrides logged with reason codes and preserved in the audit trail, keeping every file defensible.
Yes. Case outputs and risk flags flow into your existing stack, Jack Henry, Fiserv, FIS, and your compliance management systems, via secure integrations.
Yes. Available under NDA as part of your vendor management or procurement review.
Each playbook applies the requirements specific to that function, FinCEN anti-money laundering criteria for SAR filing, Reg E timelines for fraud resolution, Reg CC rules for deposit holds.
Yes. Every investigation runs inside your institution's governed environment, PII, transaction records, and case documentation stay under your control from intake to closeout, with no model training on customer documents unless agreed in writing.