AI for Compliance in Banking: 8 Best Tools for Banks and Credit Unions [2026]
Compare the 8 best AI tools for regulatory compliance in banking, from AgentFlow to Hyperproof: auditability, human oversight, deployment, and pricing.
Best for full-stack regulatory compliance automation: AgentFlow
Best for regulatory change management: Archer Evolv Compliance (formerly Compliance.ai)
Best for AI governance and model explainability: IBM watsonx.governance
Best for credit union compliance management: ViClarity
Best for SOC 2 and ISO automation in fintechs: Sprinto
Best for internal financial controls: Quantivate, an Ncontracts company
Best for operational risk and audit readiness: Hyperproof
Best for AI regulatory agents in cross-border regimes: OnFinance AI
Get 1% smarter about AI in financial services every week.
Receive weekly micro lessons on agentic AI, our company updates, and tips from our team right in your inbox. Unsubscribe anytime.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
SR 11-7 is gone, and NCUA has no AI rule. The eight AI compliance tools banks and credit unions are actually evaluating in 2026, and the criteria that decide it. That last point changed this year. On April 17, 2026, the Federal Reserve, OCC, and FDIC issued revised model risk guidance that supersedes and replaces SR 11-7, the letter nearly every vendor still cites in its compliance marketing. Most buyer guides have not caught up.
This guide covers the evaluation criteria that matter now, what NCUA expects from credit unions buying AI, and how the eight platforms compare.
What Should Banks and Credit Unions Look for in AI Tools for Compliance?
Compliance teams start with features. Regulators start elsewhere.
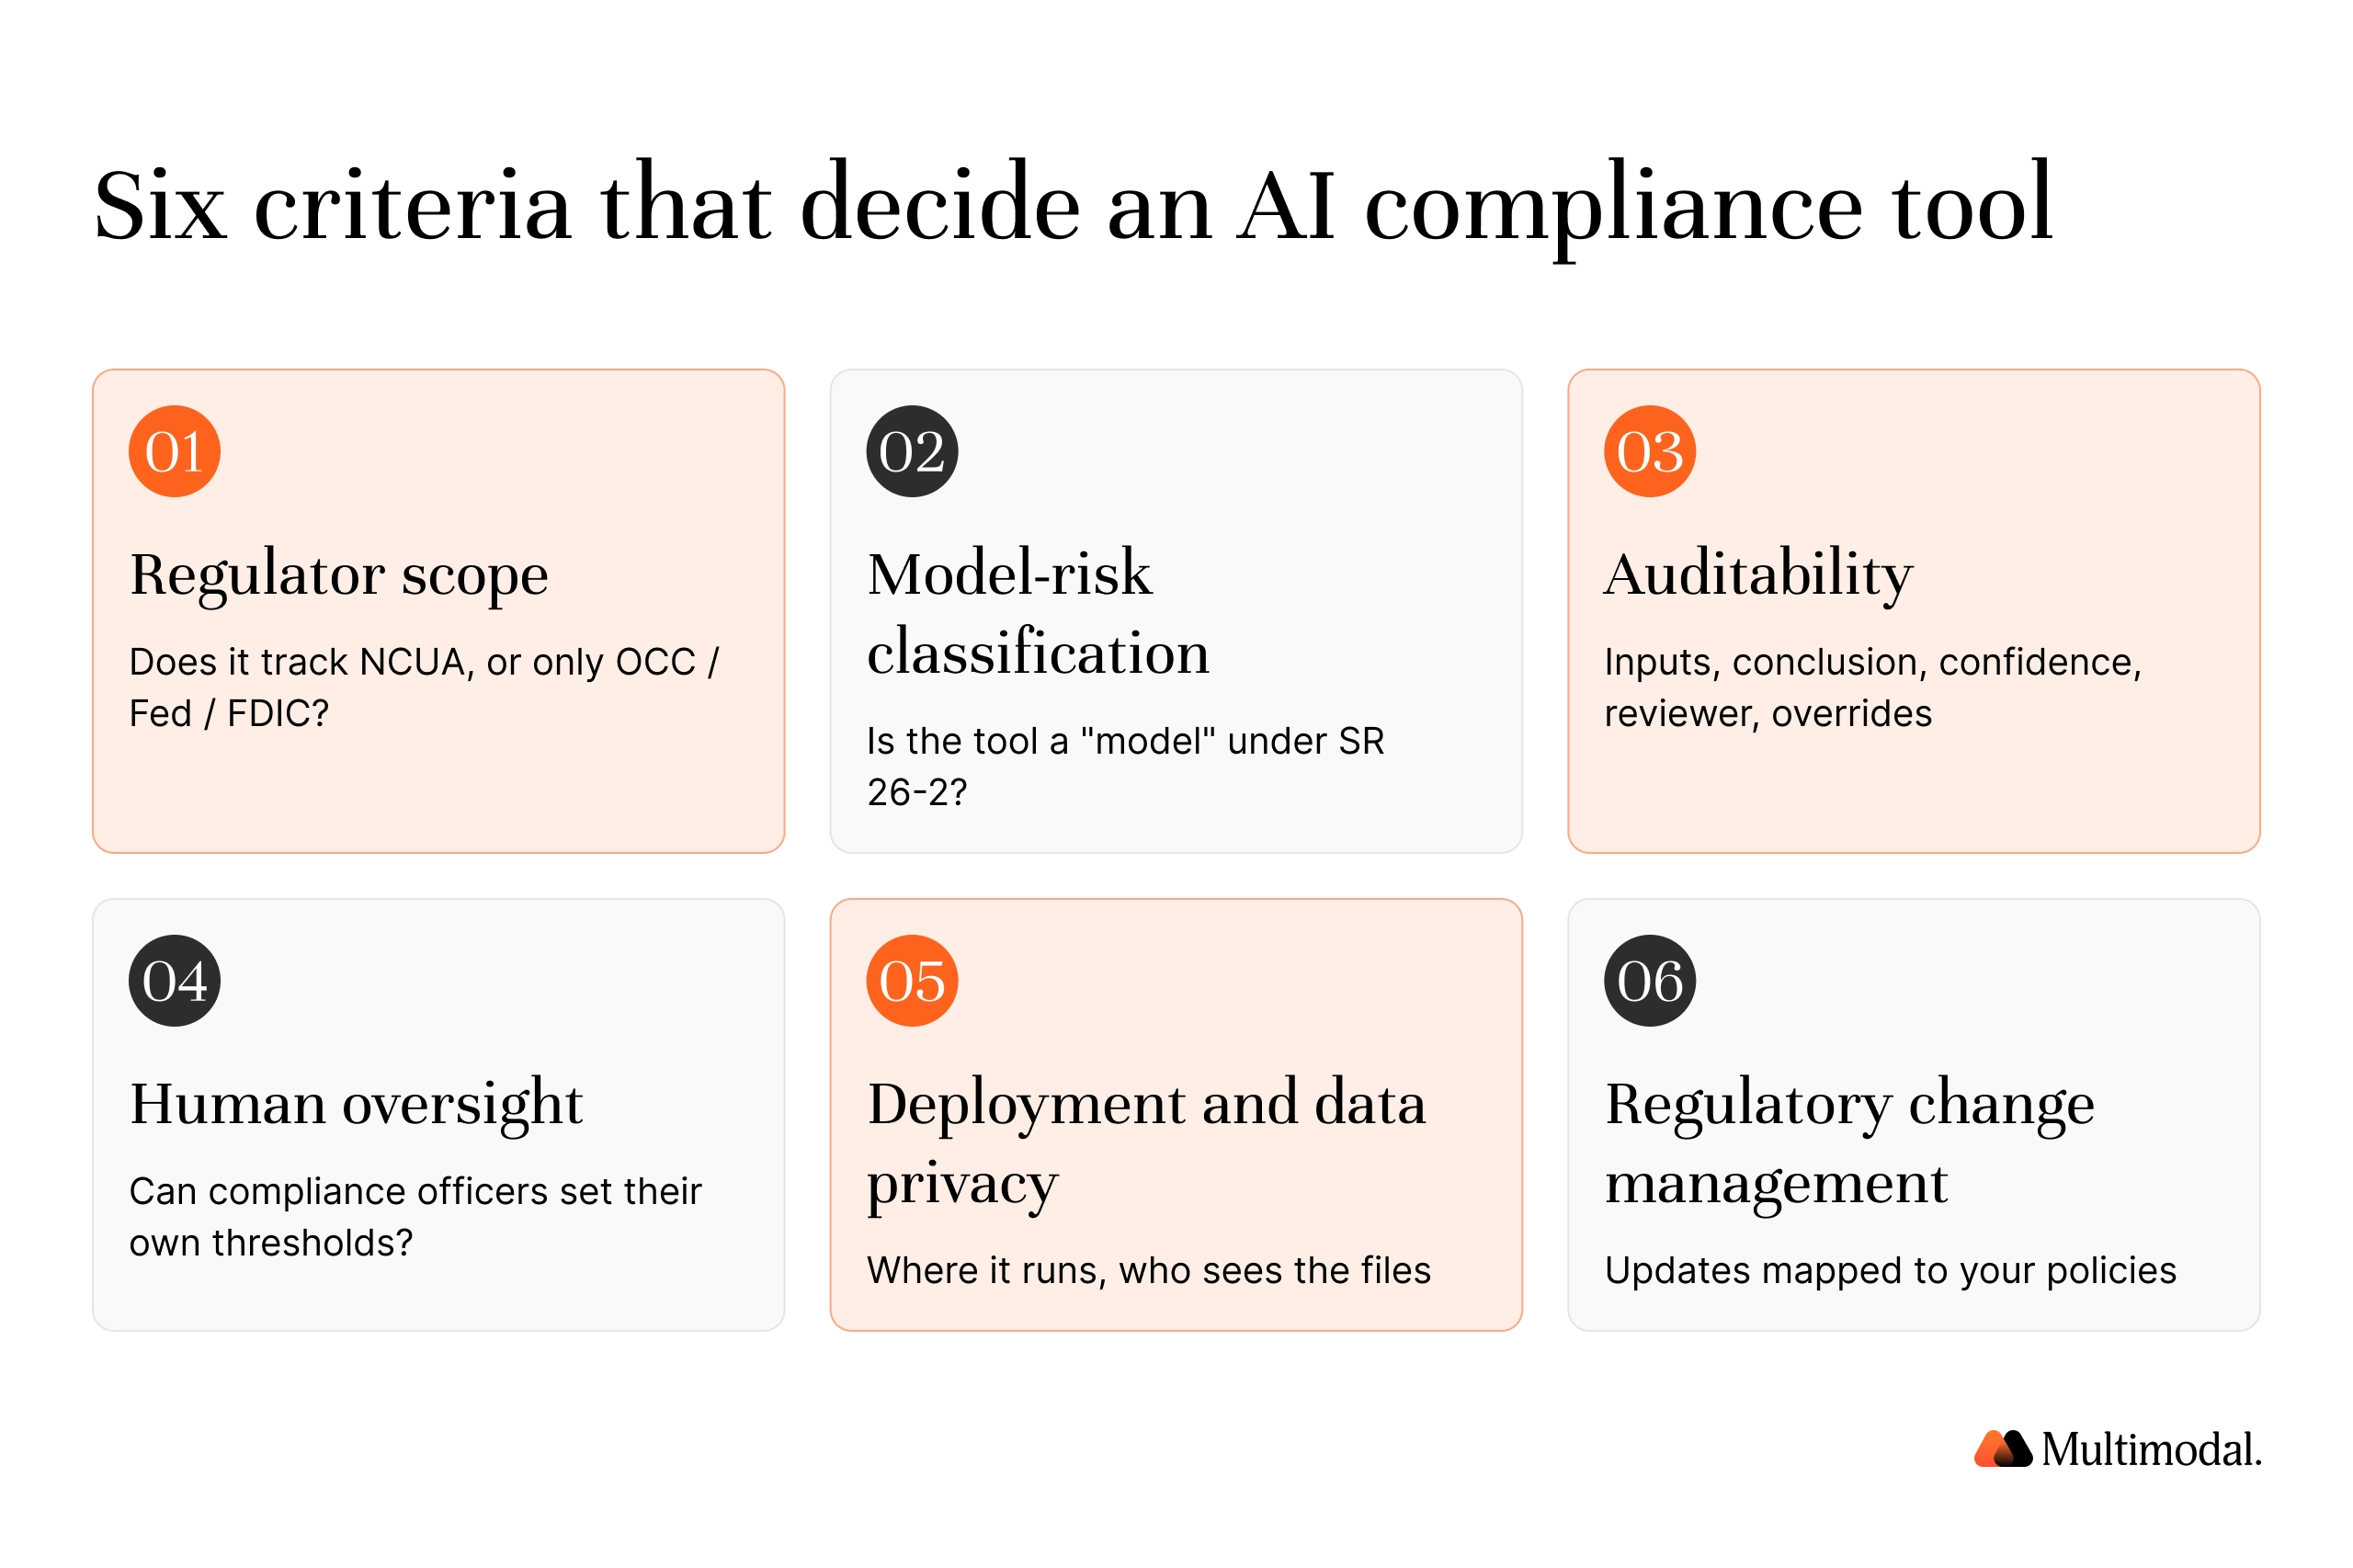
Six criteria decide:
Regulator scope: A platform built for OCC, Federal Reserve, and FDIC expectations is not automatically built for NCUA's. Ask which agencies the content library tracks.
Model-risk classification: Ask whether the product is a "model" under the 2026 guidance, which excludes "deterministic rule-based processes and software." Few vendors answer in writing.
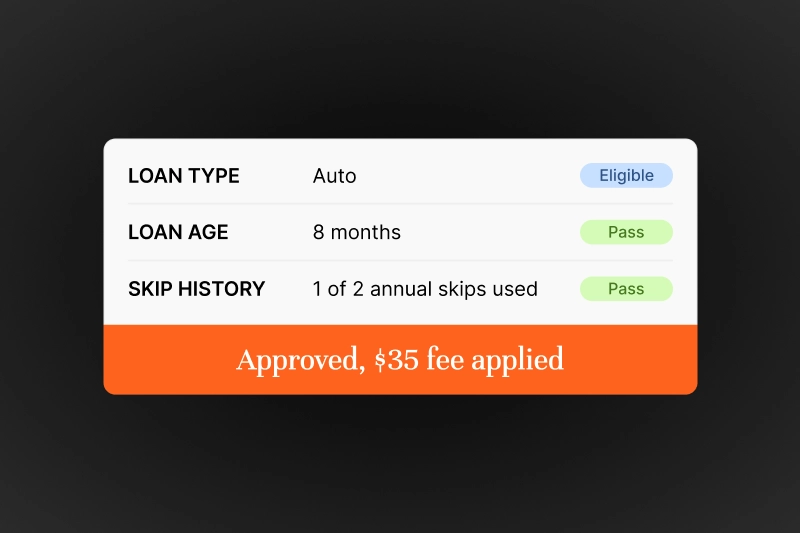
Auditability and regulatory adherence: Every AI-driven decision needs a record an examiner can follow: inputs, conclusion, confidence, reviewer, overrides. The OCC names "lack of explainability" as a distinct generative AI risk.
Human oversight: The OCC observes banks limiting AI to "specific use cases with guardrails and human-in-the-loop accountability." Compliance officers should set those thresholds, as our confidence scoring guide covers.
Deployment and data privacy: Where the model runs, whether your files train it, and whether you have the right to audit determine usability.
Regulatory change management: AI can analyze vast regulatory content to identify updates in real time, taking routine compliance tasks off compliance professionals and helping mitigate risk early.
"Although you may utilize a vendor to provide a certain product or service, you can't outsource the risk... even if you use a third party to offer that product or service, whether that's something that's internal for internal operations or something that's more member-facing, you're still on the hook for that at the end of the day." — Michael Heller, Associate Attorney, Messick Lauer & Smith
The vendor's controls become your controls, which is why third-party risk management is often the weakest link in compliance programs.
Is SR 11-7 Still the Standard for AI Compliance Tools in 2026?
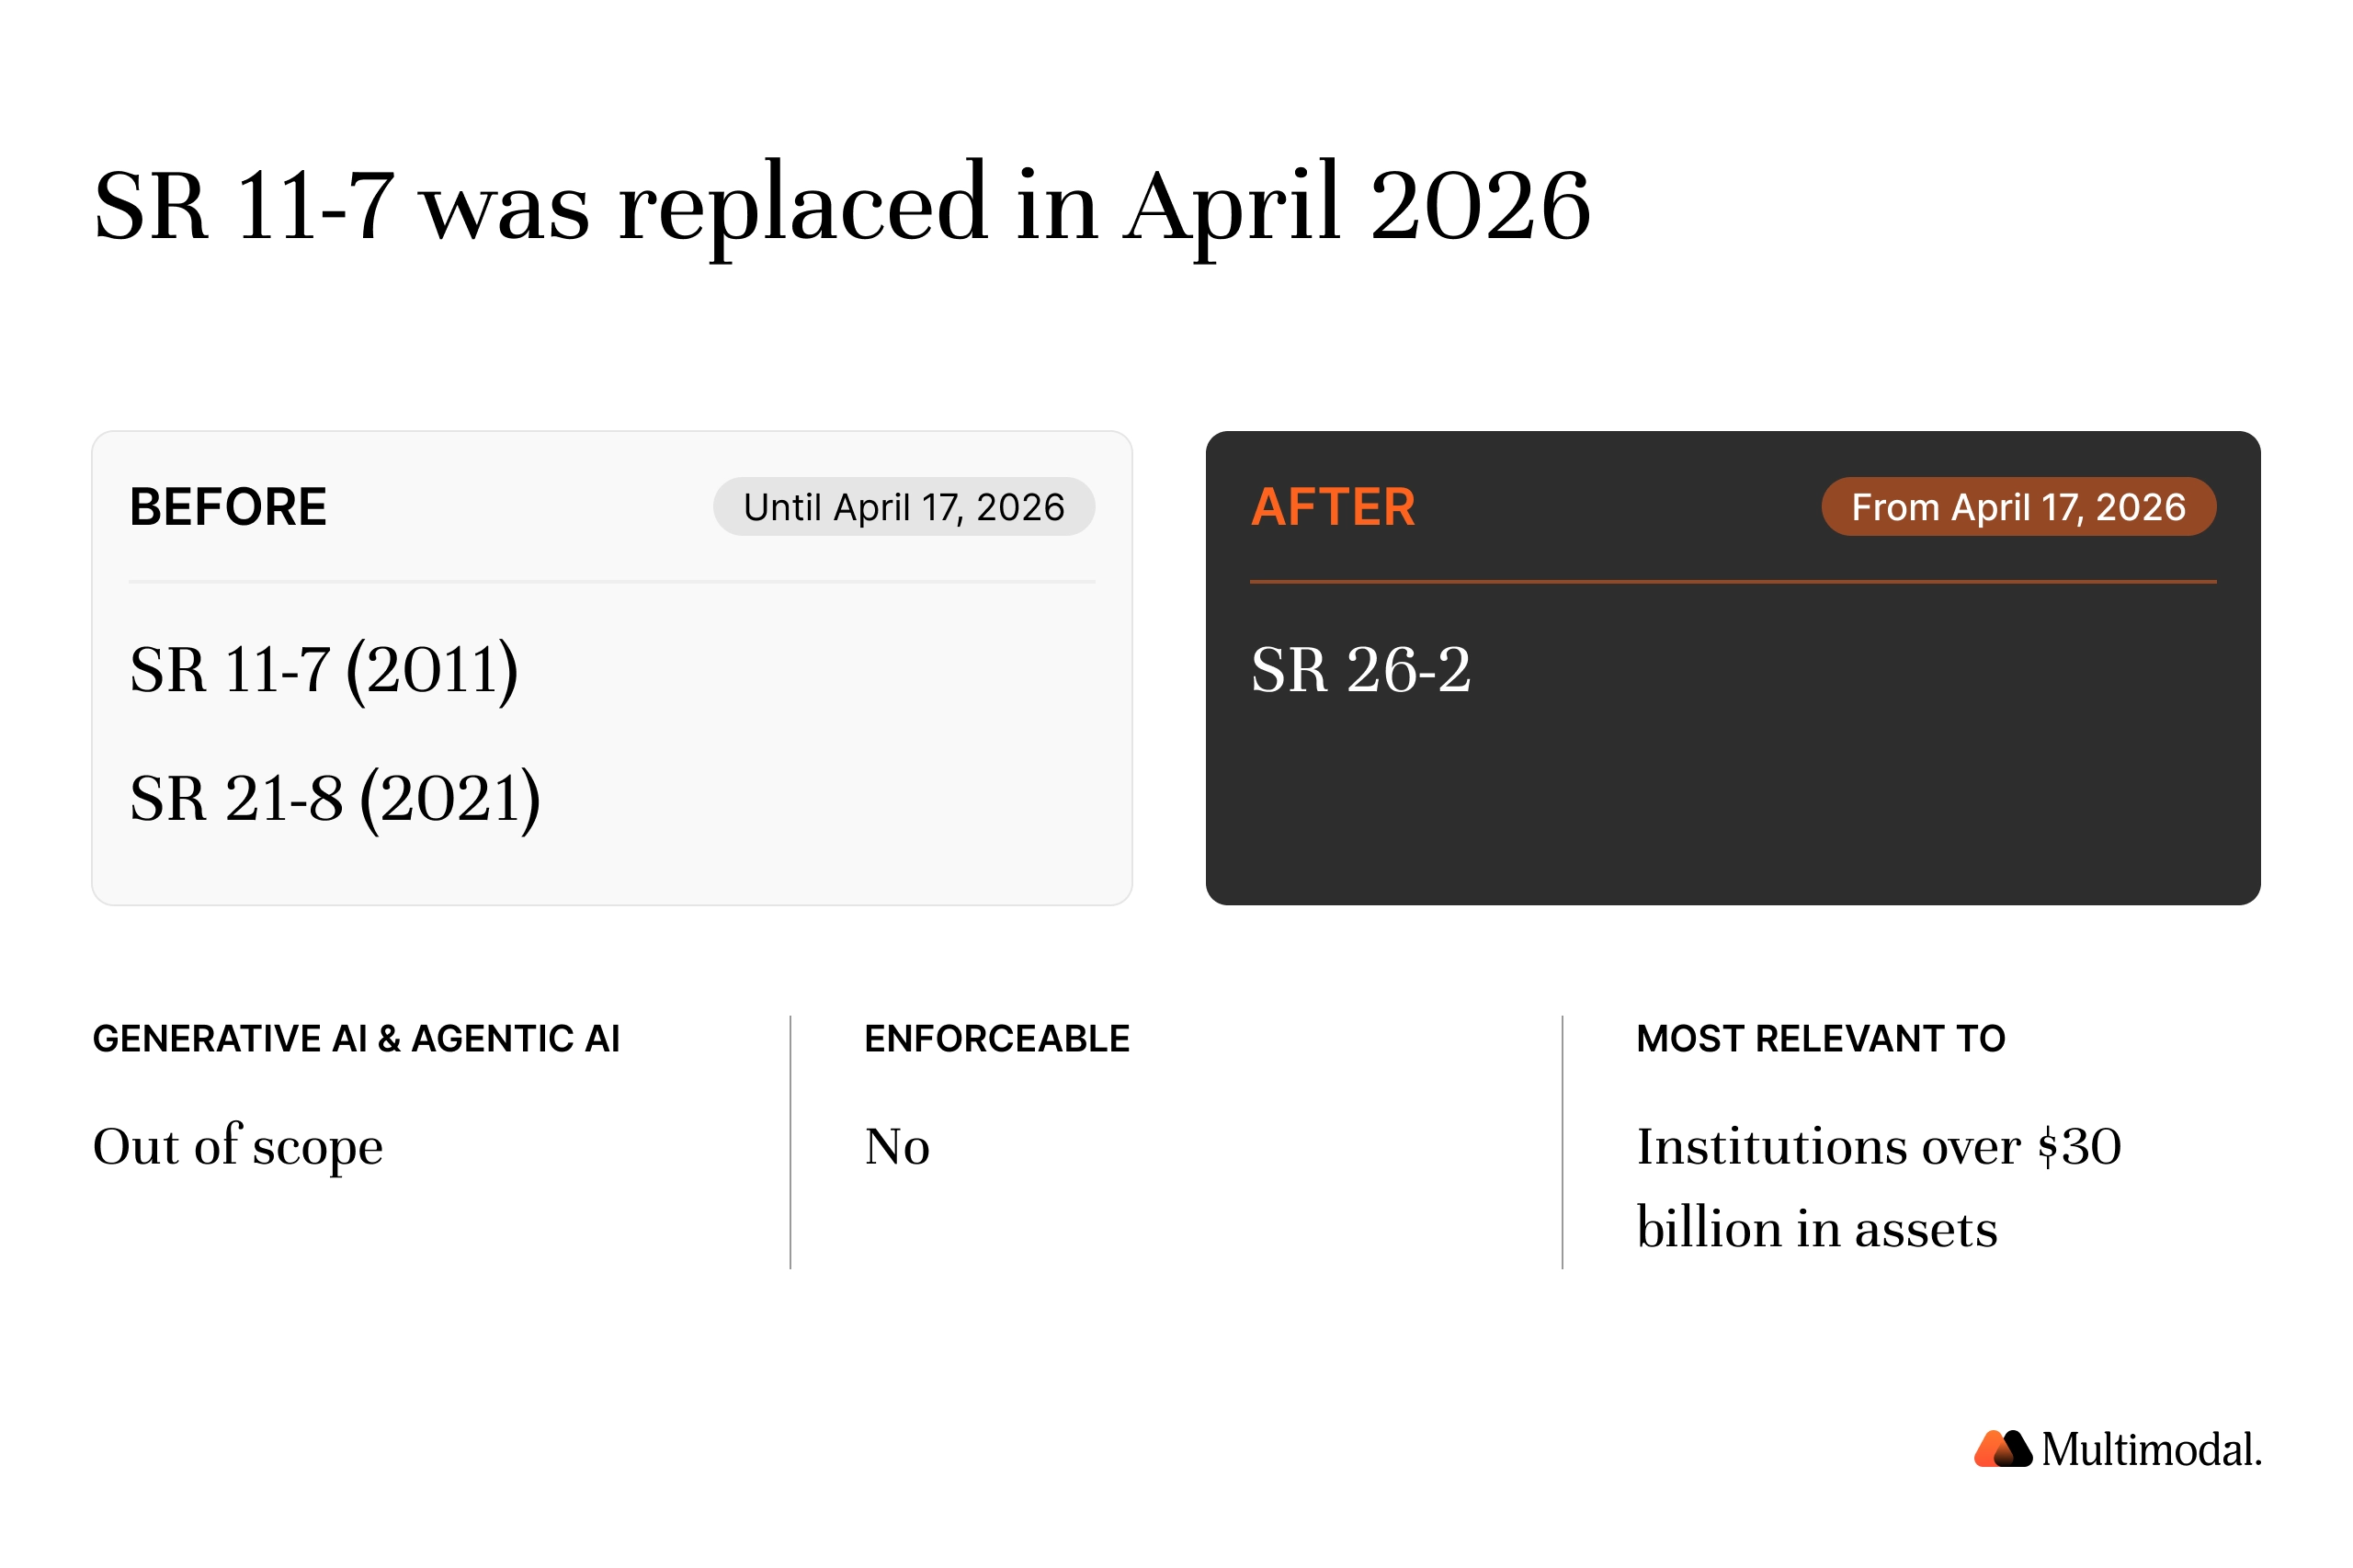
No. SR 11-7 was superseded on April 17, 2026, by SR 26-2, the revised interagency Guidance on Model Risk Management, which also replaced SR 21-8, which covered BSA/AML systems. Three details matter when you are buying:
Generative AI and agentic AI are out of scope. The OCC's announcement is unambiguous: "Generative AI and agentic AI models are novel and rapidly evolving. As such, they are not within the scope of this guidance." A request for information on banks' use of AI is planned. So a vendor claiming its agentic platform is "SR 26-2 compliant" is describing something the guidance does not address.
It is not enforceable. SR 26-2 states it "does not set forth enforceable standards or prescriptive requirements," and is "expected to be most relevant to banking organizations with over $30 billion in total assets."
Vendor products still have to be validated. The guidance keeps the clause that matters most for buyers: "An important element of model risk management is the validation of vendor products, either by internal or outside parties." Buying does not transfer the work.
For context, the FFIEC IT handbook booklet vendors cite for "FFIEC alignment" was issued in June 2021, before generative AI existed.
What Does NCUA Expect From a Credit Union's AI Compliance Tool?
Asked whether it has AI-specific regulations, NCUA answers: "No. NCUA has not issued AI-specific rules or regulations. However, existing regulations are technology-neutral and apply to AI use." It adds that "AI is not treated differently than any other innovative technology. Our supervisory focus is on risk management, not the tool itself."
That reframes the purchase. There is no AI checklist to pass. There is your risk management framework, the risk assessment you run on any material vendor, and the question of whether this tool fits within both.
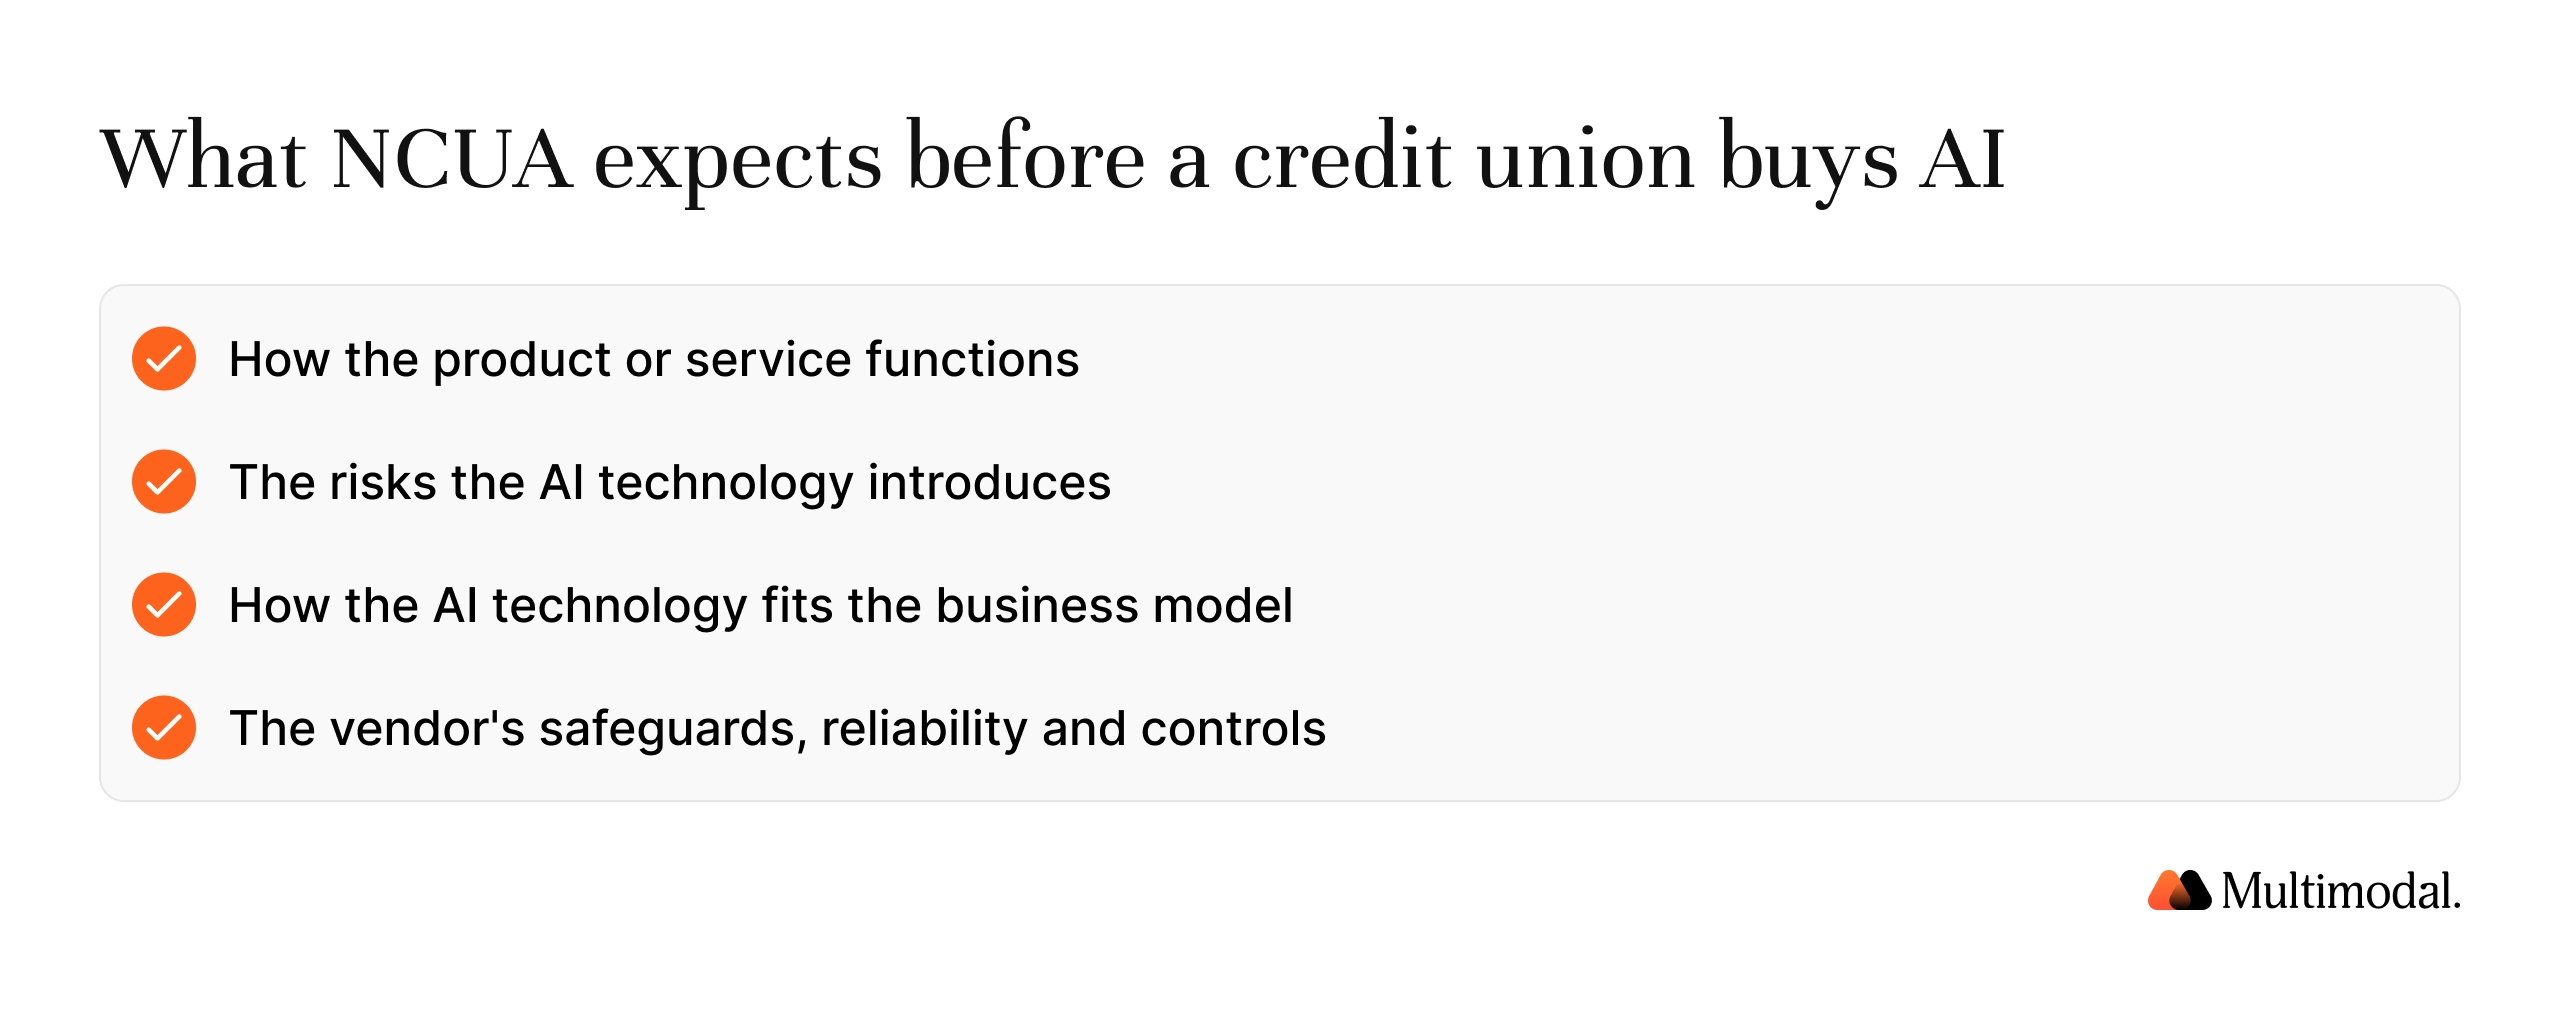
NCUA's vendor expectations read like a buyer's checklist: understand how the product functions, the risks the AI technology introduces, how it fits the business model, and the vendor's safeguards, reliability, and controls. Letters 07-CU-13 and 01-CU-20 carry the mechanics.
One correction, because it circulates widely: NCUA's 2026 Supervisory Priorities letter does not name AI. Its priorities are balance sheet management, operational risk, and compliance risk management.
"If anybody's had an audit recently, the most you're gonna get from an NCUA auditor right now is, let me see your AI governance policy. Do you have some documentation around this? They haven't yet come in and started saying, show me how your AI agents work and show me that you're validating the data. Show me that you're not discriminating." — Jeffrey Staw, Chief Information and Innovation Officer, Firefighters First Credit Union
That gap is the buying window. The tool you choose today is the documentation you hand over when examiners do start asking, so pick one whose audit trail you would be comfortable printing.
How We Evaluated These AI Compliance Tools
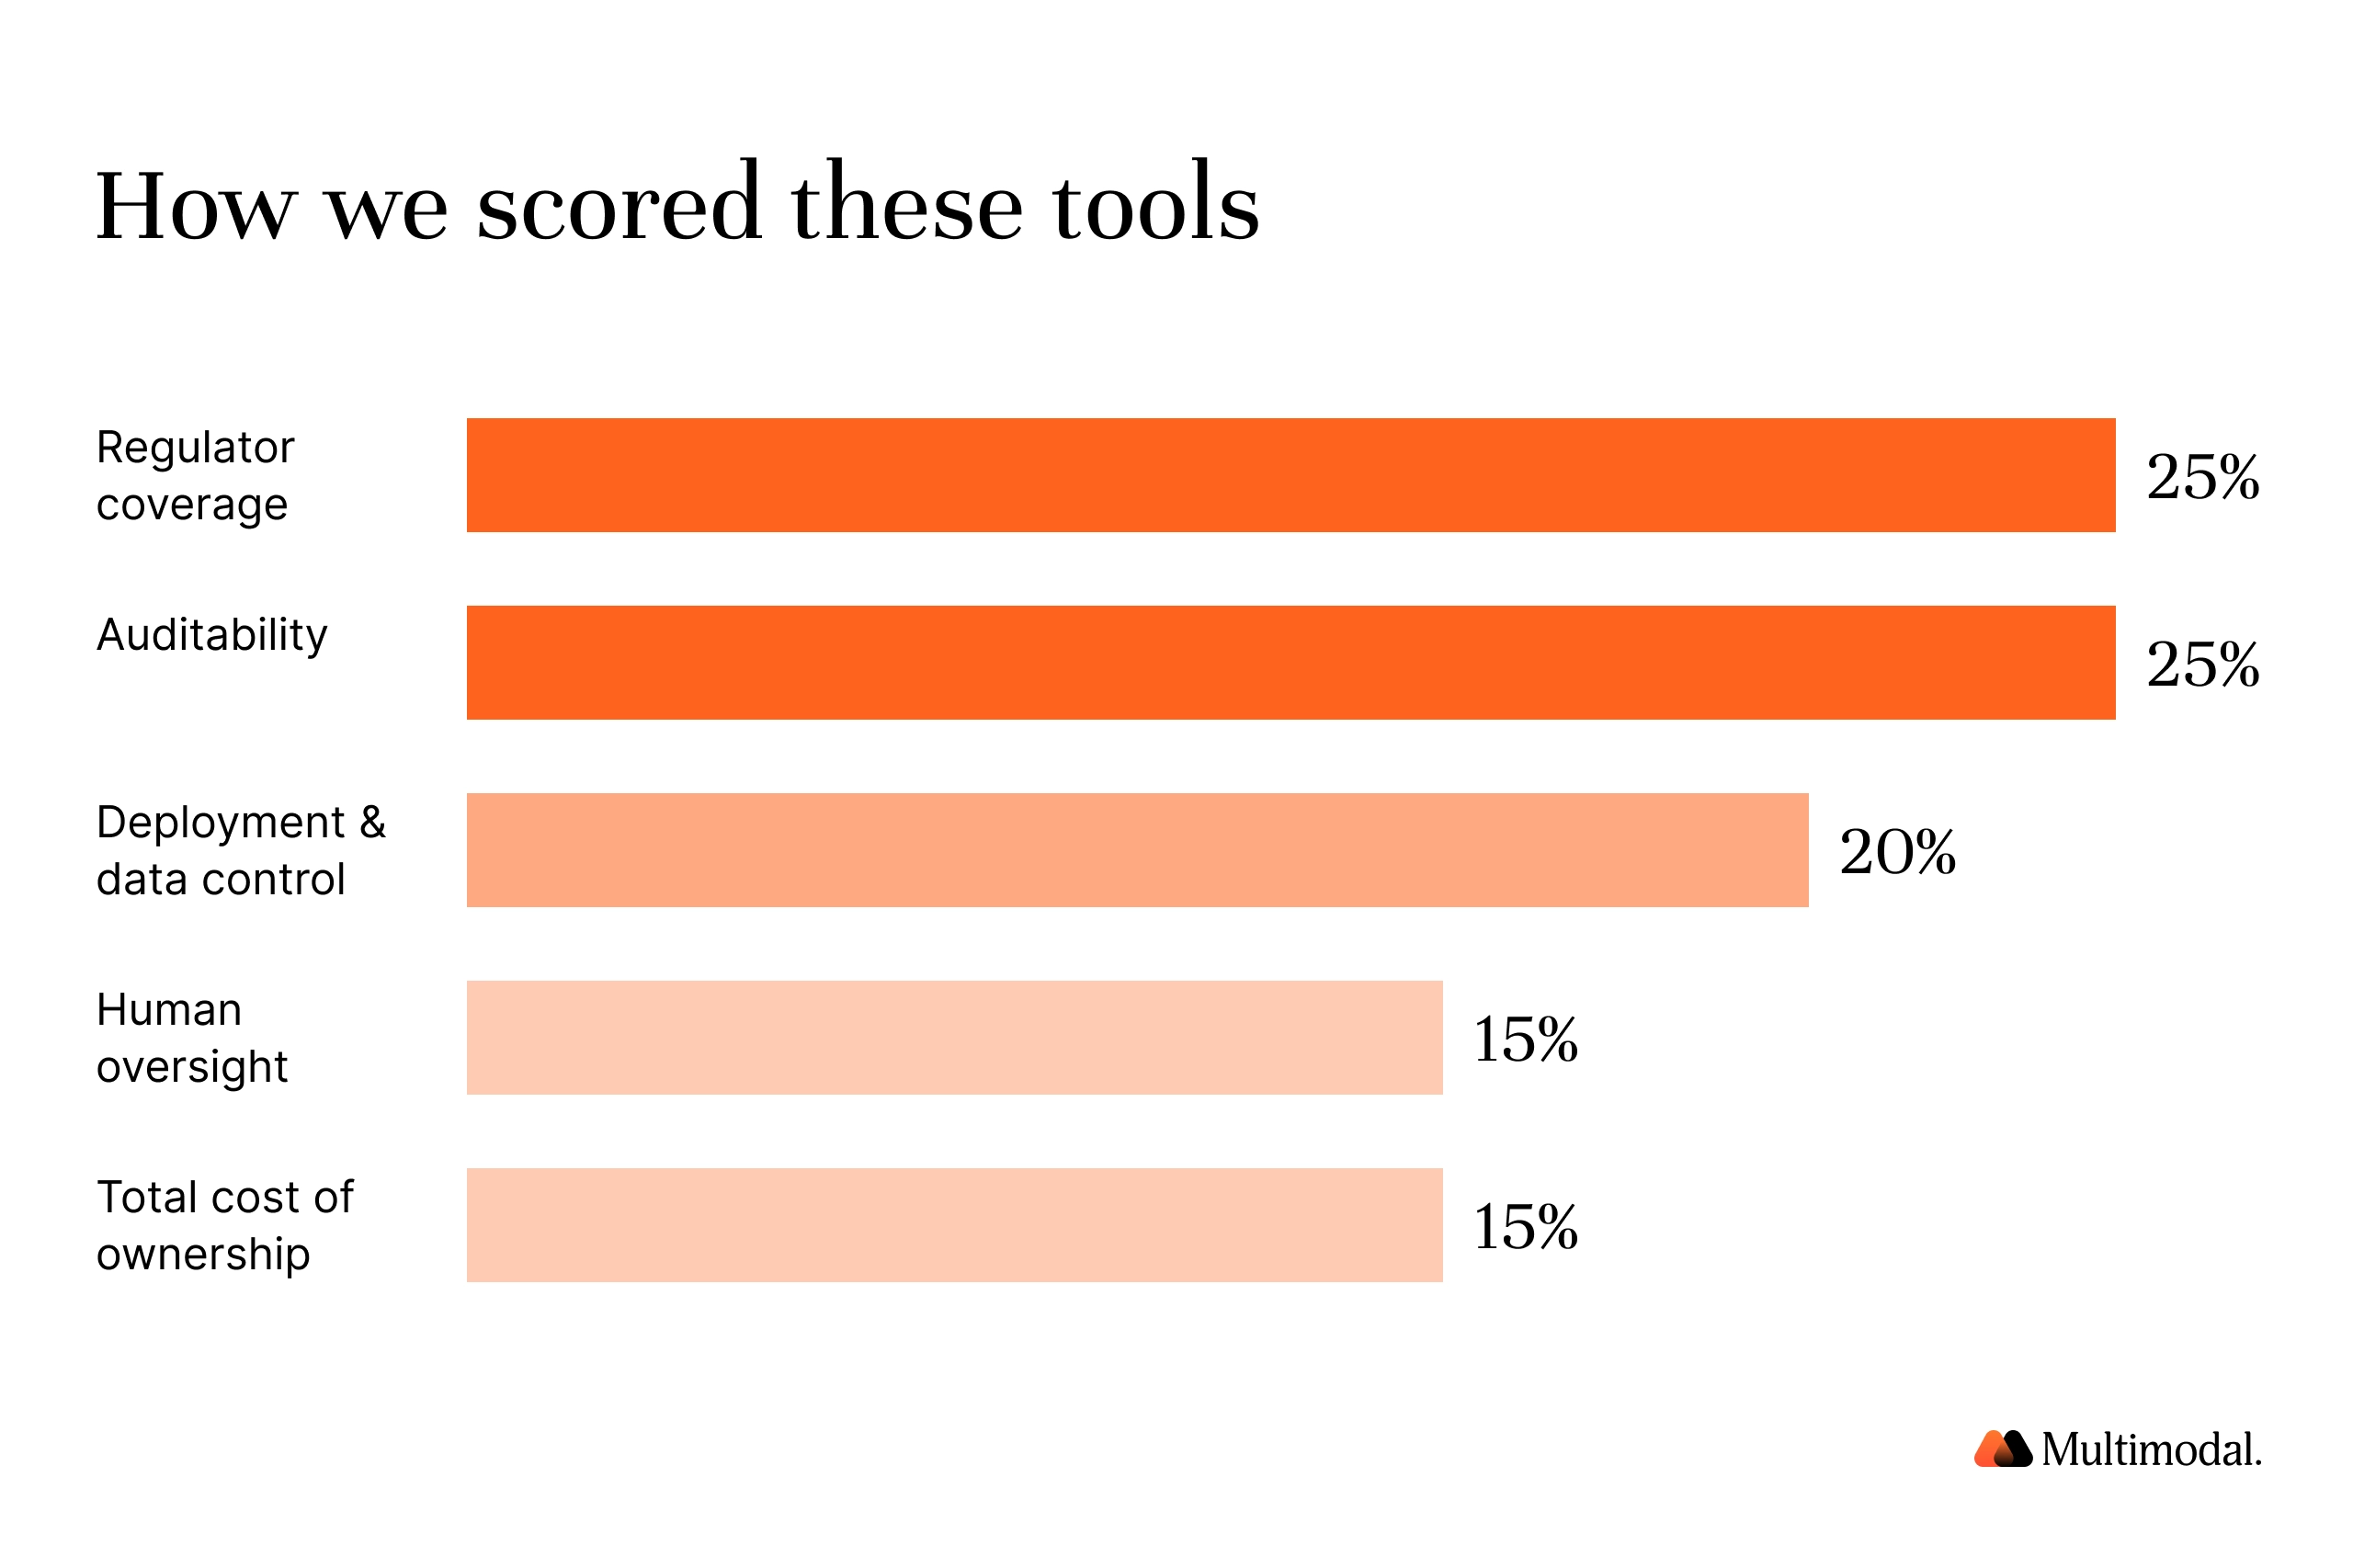
Five weighted criteria, applied to every platform below:
Regulator coverage (25%): which regulatory frameworks and agencies the content and controls actually track, including NCUA.
Auditability (25%): depth of the decision record, and whether the tool can explain a conclusion.
Deployment and data control (20%): hosting options, data privacy posture, no-train commitments, right to audit.
Human oversight (15%): whether compliance officers can configure thresholds and routing themselves.
Total cost of ownership (15%): licensing plus integration, governance and audit overhead.
Pricing is quote-based across most of this category, so we compare pricing model rather than list price.
The 8 Best AI Compliance Tools for Banks and Credit Unions
1. AgentFlow
Multimodal's agentic AI platform for credit unions and banks runs compliance processes end-to-end rather than surfacing tasks for humans to complete. Multi-agent workflows handle intake, extraction, validation, exception routing, and reporting in accordance with your internal policies.
Compliance.ai is now part of Archer, and existing users have been migrated to Archer Evolv Compliance, so evaluate it under that name. It remains one of the strongest options for regulatory change management.
Key Features
Regulatory intelligence across federal and state agencies
Automated mapping of regulatory changes to internal policies and controls
Review, assignment and attestation workflow
Integration with the wider Archer GRC suite
Best For
Compliance leaders who need to track evolving regulations across multiple regulatory frameworks without reading every release themselves.
Pros
Deep regulatory content library
Strong change-to-control mapping rather than a raw feed
Enterprise GRC integration through Archer
Cons
Change management is the core strength, so it does not cover transactional compliance monitoring
Rebrand means older documentation and reviews still reference Compliance.ai
Pricing:
Enterprise, quote-based.
3. IBM watsonx.governance
IBM was named a Leader in the first Gartner Magic Quadrant for AI Governance Platforms, published June 17, 2026. This governs your AI rather than doing compliance work.
Key Features
Model inventory and lifecycle governance
Bias, drift and performance monitoring
Explainability tooling for model outputs
Policy enforcement across machine learning and generative AI
Best For:
Institutions that need a governance framework and documented responsible AI practices across a growing model estate, especially where risk, compliance and legal teams review together.
Pros
Strong analyst validation in a newly defined category
Deep explainability and transparency reporting
Maps cleanly to model risk management expectations
Cons
Governs models, does not execute compliance tasks
Heavier lift than lean compliance teams typically want
Pricing
Enterprise, quote-based.
4. ViClarity
ViClarity is one of the few platforms in this category built with credit unions in mind, and it launched AI-powered regulatory monitoring in April 2026 aimed squarely at that audience.
Key Features
Compliance management, internal audit and vendor management modules
AI regulatory monitoring
Board and committee reporting
Issue tracking and remediation workflow
Best For:
Credit unions and community banks that want compliance management, compliance audits and third-party risk management in one system.
Pros
Genuine credit union orientation rather than a relabel
Reporting built for boards and examiners
Approachable for lean compliance teams
Cons
Not designed for high-volume transaction monitoring
Narrower AI depth than the AI-first platforms here
Pricing
Modular, quote-based.
5. Sprinto
Sprinto automates security and privacy compliance programs and repositioned around an autonomous trust platform in March 2026. It reports serving 3,000+ customers across 75 countries and offering 300+ integrations.
Key Features
Continuous control monitoring
Automated evidence collection
SOC 2, ISO 27001, GDPR and adjacent compliance regulations
Broad integration coverage across cloud tooling
Best For
Fintechs and bank technology partners proving security posture to institutional buyers.
Pros
Fast time to audit readiness
Automates routine compliance tasks with little manual setup
Wide integration library
Cons
Security and privacy frameworks rather than banking regulatory requirements
No NCUA or bank examiner orientation
Pricing
Subscription, quote-based.
6. Quantivate, an Ncontracts Company
Quantivate has been part of Ncontracts since December 2023 and continues to ship under its own name. Its strengths are internal controls and enterprise risk management for financial institutions.
Key Features
Enterprise risk management and risk assessment
Internal controls and policy management
Vendor management and business continuity
Board reporting
Best For
Banks and credit unions building a single risk and compliance system of record.
Pros
Built for financial institutions from the start
Broad module coverage across risk and compliance
Strong policy and controls lineage for audits
Cons
Breadth means longer configuration
AI capability is narrower than the AI-first tools here
Pricing
Modular, quote-based.
7. Hyperproof
Hyperproof focuses on operational compliance and audit readiness, and acquired Expent.ai in 2025 to extend its vendor risk capability.
Key Features
Control and framework management
Automated evidence collection and freshness tracking
Risk register and issue management
Cross-framework control mapping
Best For:
Compliance teams managing multiple regulatory standards simultaneously and preparing for recurring compliance audits.
Pros
Excellent evidence workflow
Cross-framework mapping removes duplicate work
Improves documentation accuracy and audit readiness
Cons
Compliance operations rather than banking regulatory intelligence
Requires an owner to maintain the control library
Pricing
Custom, no published tiers.
8. OnFinance AI
OnFinance AI builds AI regulatory agents for financial institutions, with particular depth in Indian and Gulf regulatory regimes through its NeoGPT product.
Key Features
Regulatory agents for monitoring and reporting
Jurisdiction-specific regulatory content
Workflow automation for compliance professionals
Audit logging on agent actions
Best For
Institutions with cross-border regulatory exposure outside the United States.
Pros
Genuinely agentic design rather than a chatbot layer
Strong non-US regulatory coverage
Cons
Lighter US coverage
No NCUA orientation
Pricing
Quote-based.
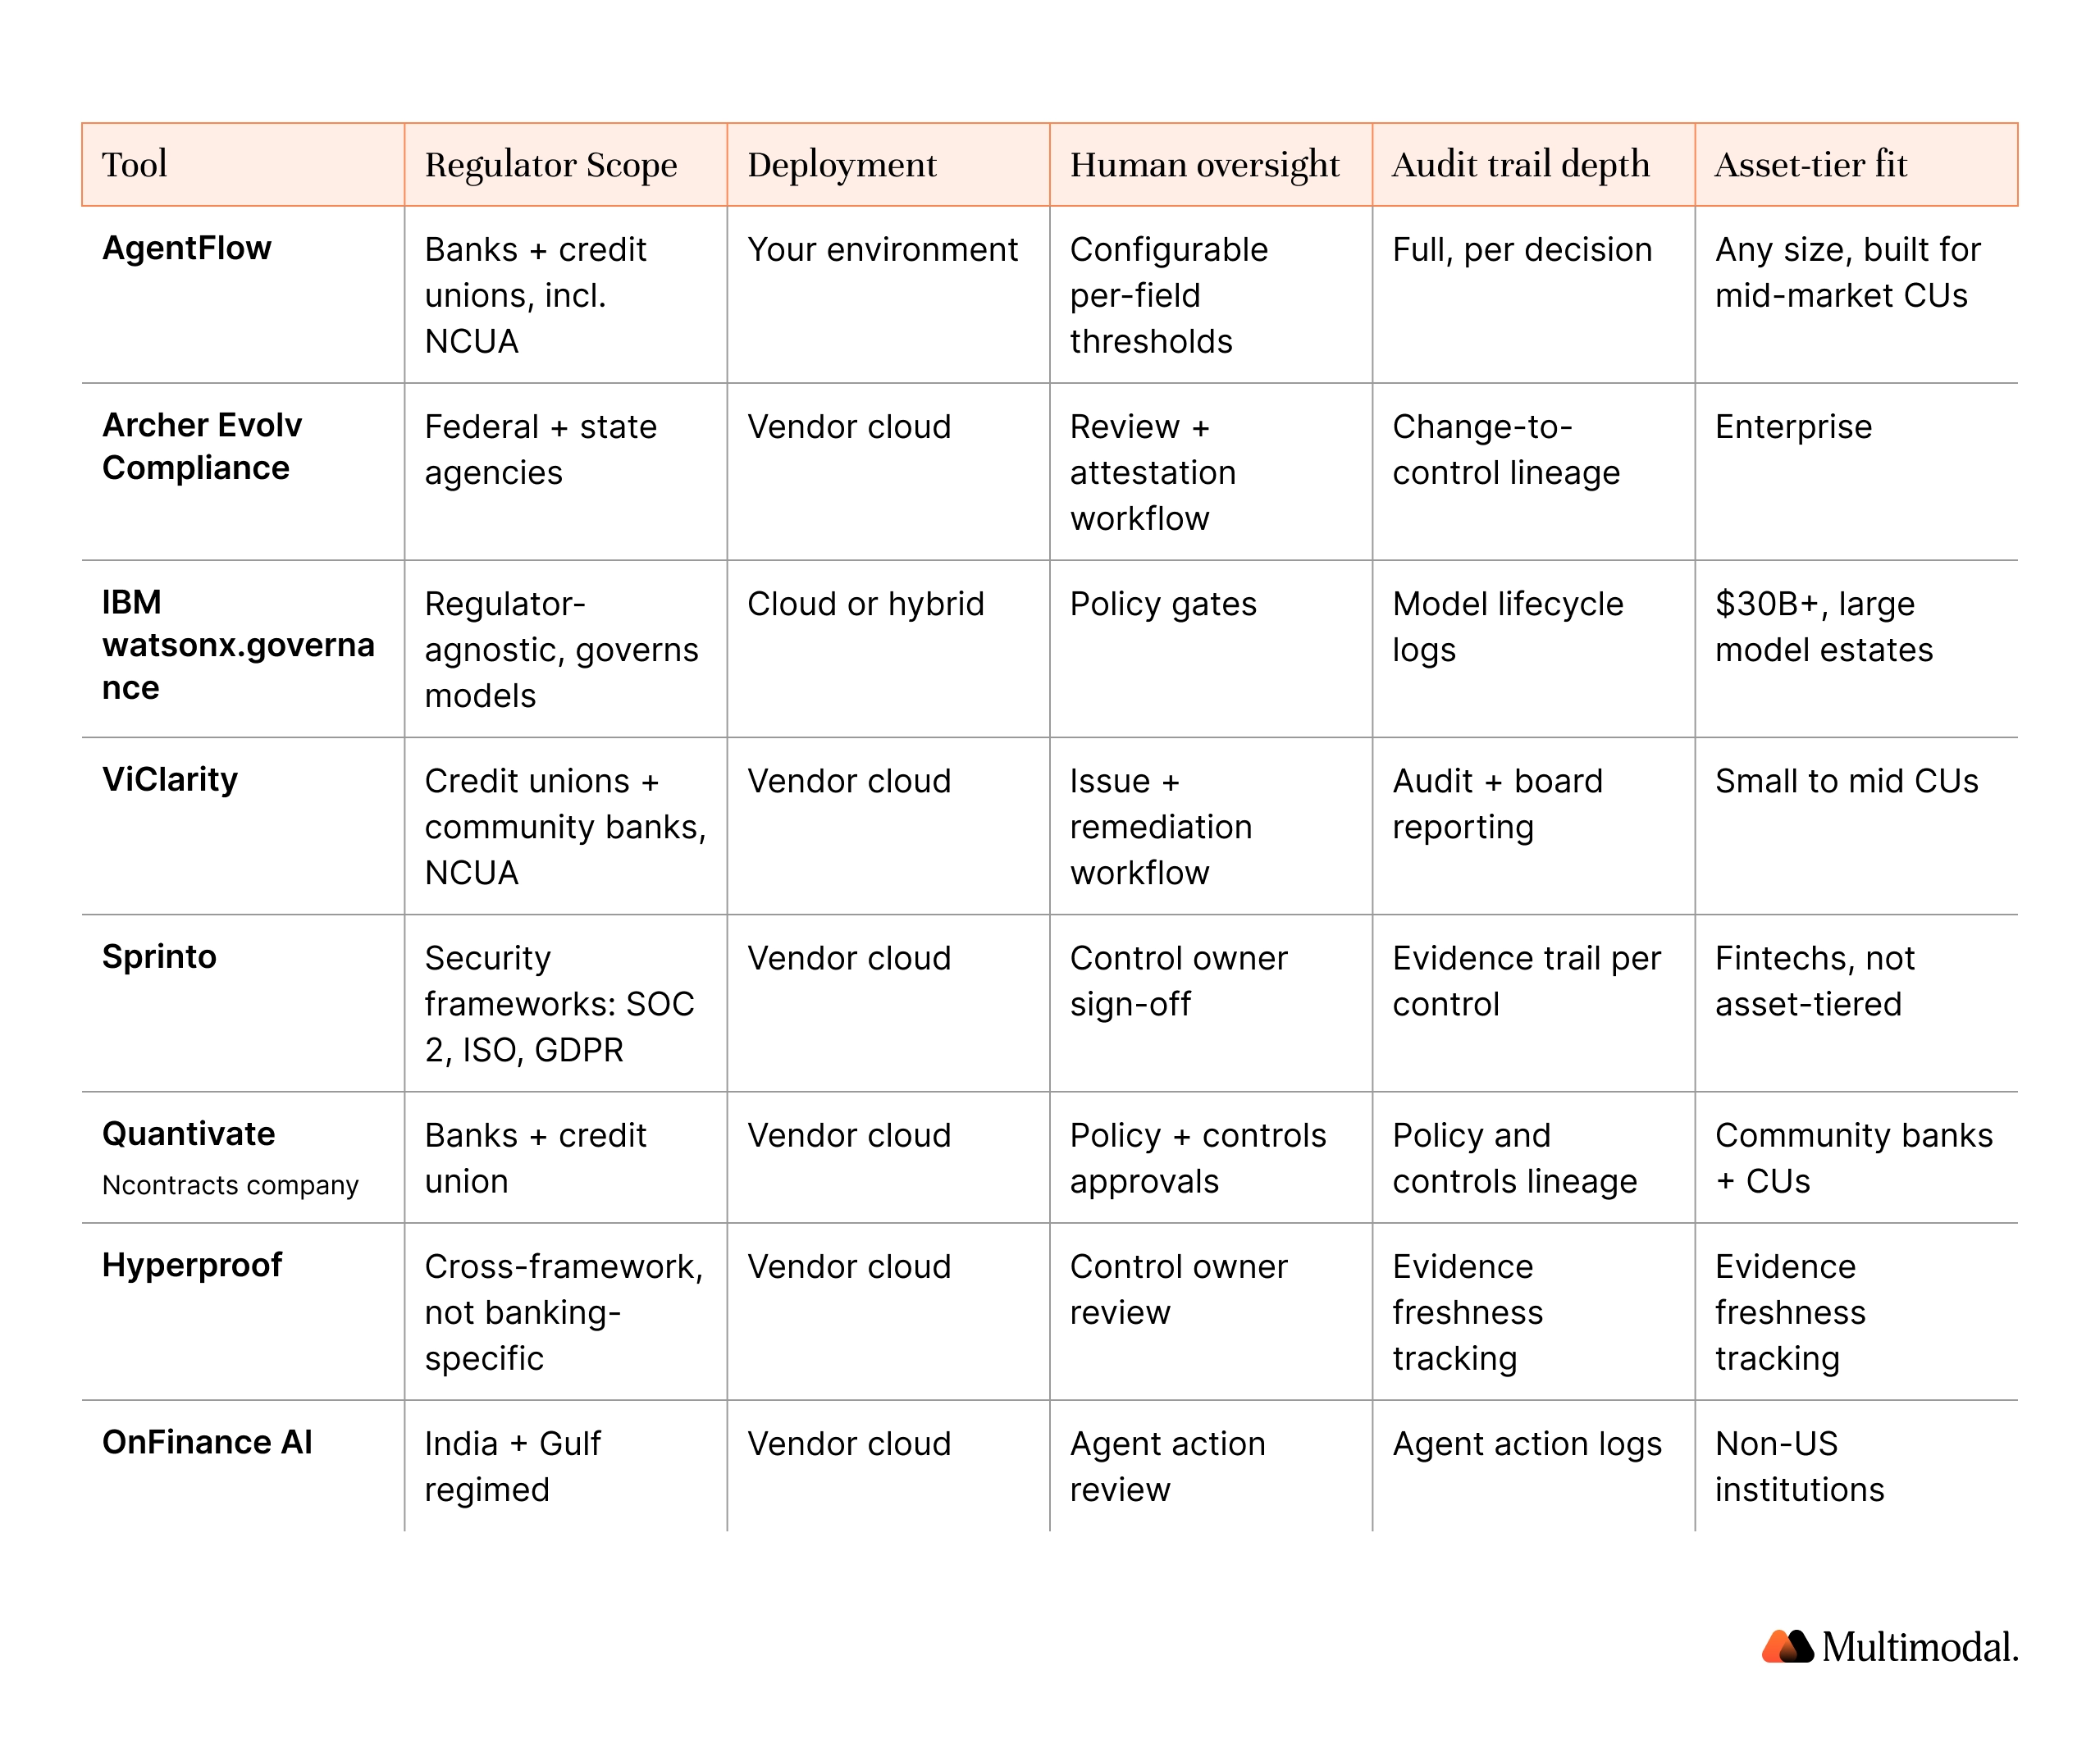
How Do the 8 Tools Compare: At a Glance
What Happens When Automated Compliance Monitoring Fails?
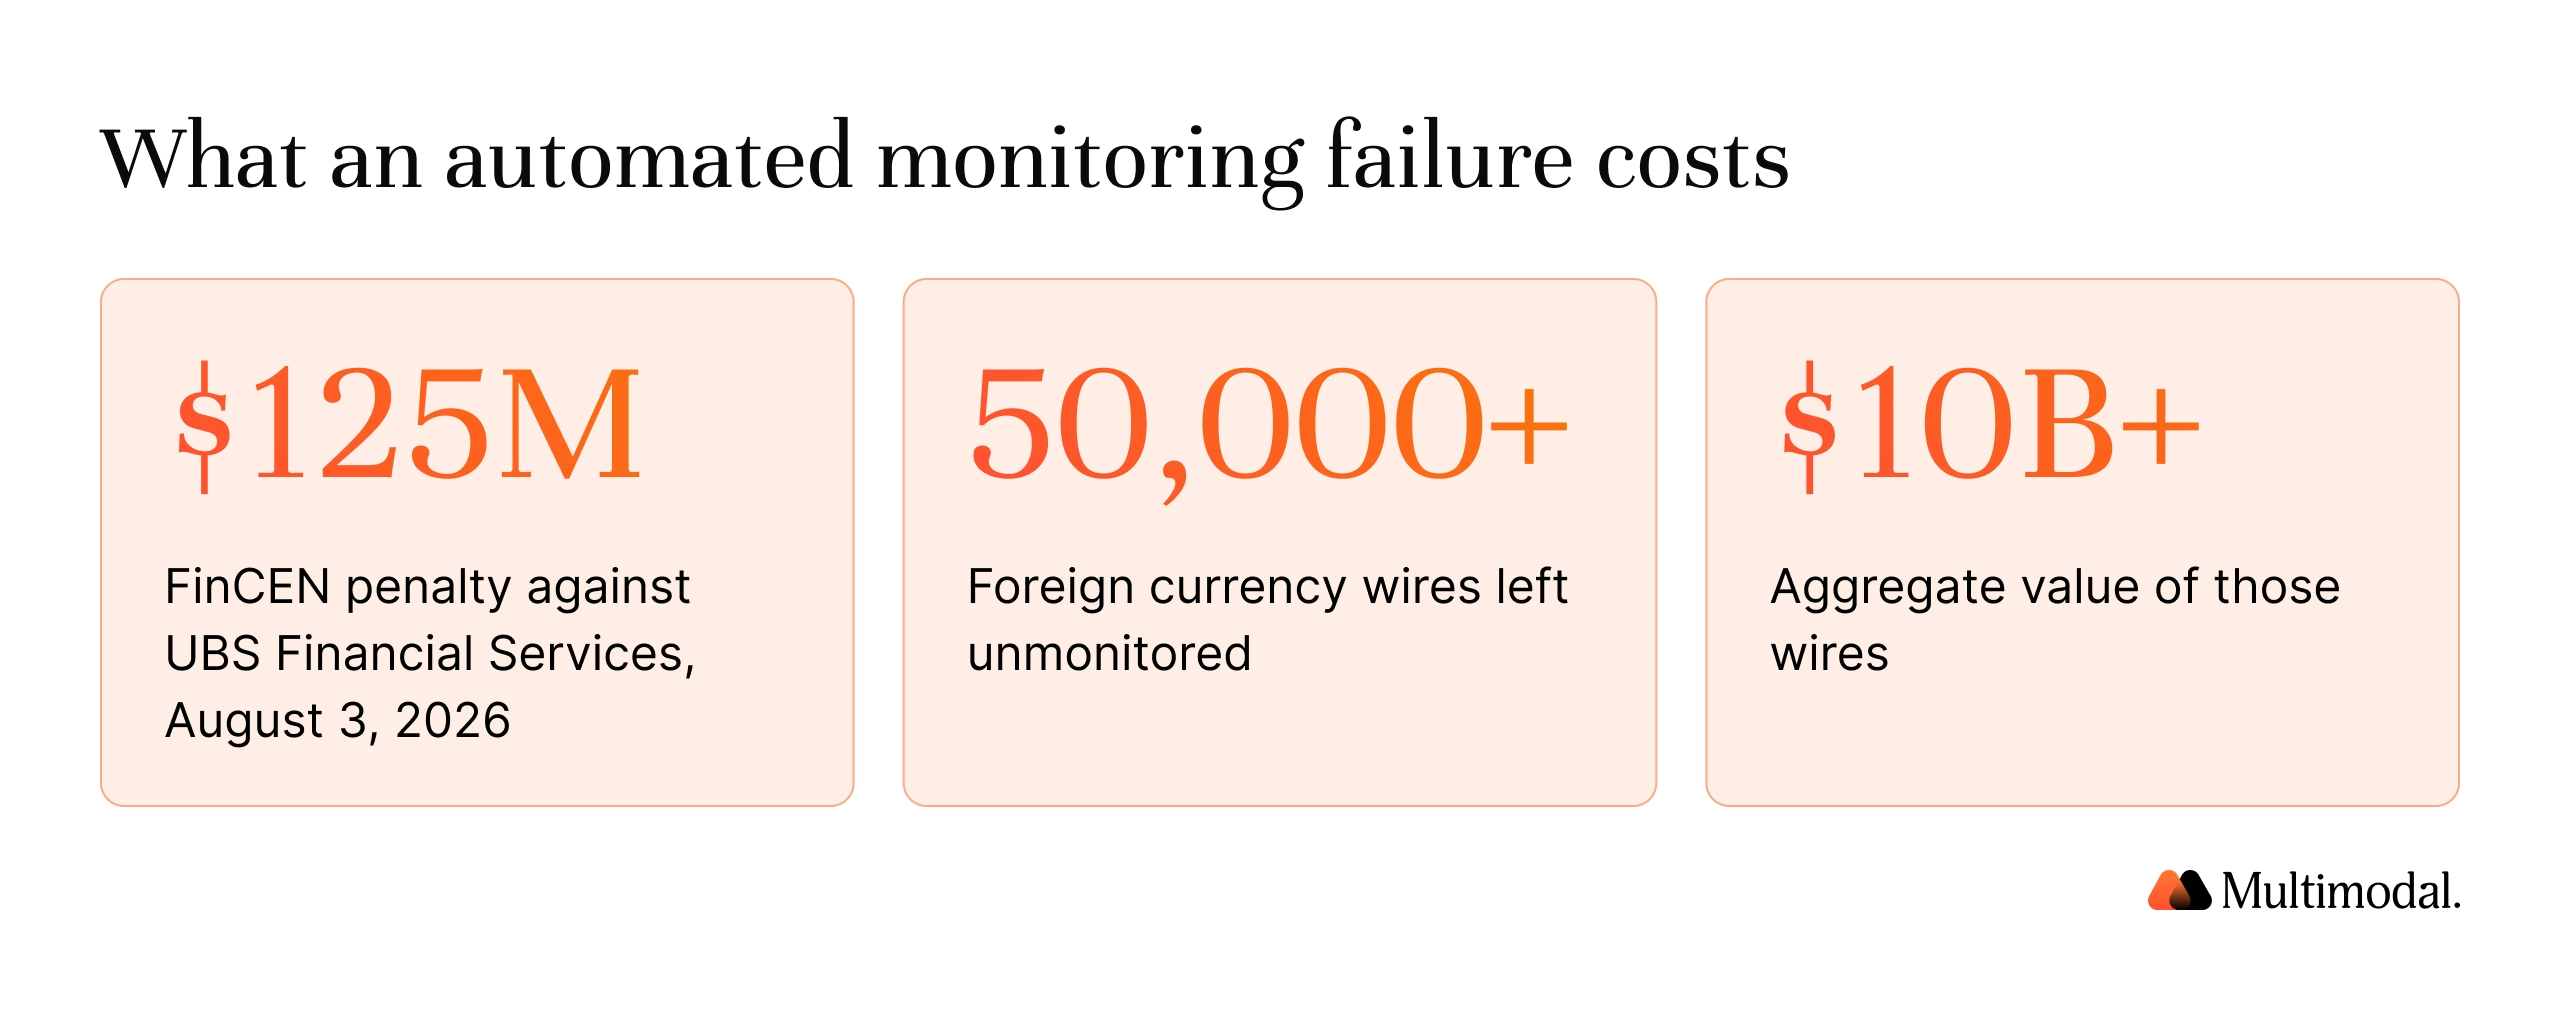
On August 3, 2026, FinCEN assessed a $125 million civil money penalty against UBS Financial Services, which it called "the largest penalty ever imposed against a broker-dealer for BSA violations to date."
The detail that matters for buyers is where it started. A 2018 consent order "found that UBSFS failed to adequately monitor foreign currency wires due to weaknesses in UBSFS's automated monitoring system." UBSFS subsequently "failed to appropriately monitor over 50,000 foreign currency wires with an aggregate value of more than $10 billion," according to FinCEN.
An automated system that silently stops covering part of the population is worse than a manual process that visibly cannot keep up. Ask what a platform does when it fails, whether coverage gaps raise alerts, and who is notified when a rule stops firing.
Can an AI Agent Handle Regulatory Reporting in Banks?
Yes, with human review at the points that carry regulatory exposure.
Regulatory reporting suits agentic automation because the work is repetitive, evidence-based, and rule-bound. Agents can pull source records, reconcile them, populate filings, flag exceptions, and assemble supporting documentation, while compliance officers approve the judgment calls.
The ground is also shifting. FinCEN issued a notice of proposed rulemaking on April 7, 2026, to reform AML/CFT programs, refocusing expectations "on effectiveness by distinguishing between deficiencies stemming from program design ('establishment') and program implementation ('maintenance')." If you are buying transaction monitoring, ask how the vendor evidences effectiveness, not just coverage.
Frequently Asked Questions
Is SR 11-7 still in effect in 2026?
No. SR 11-7 was superseded and replaced on April 17, 2026, by SR 26-2, revised interagency guidance issued by the Federal Reserve, OCC, and FDIC. SR 21-8, covering model risk for BSA/AML systems, was replaced at the same time.
Does SR 26-2 apply to generative AI and agentic AI compliance tools?
No. The OCC stated that generative AI and agentic AI models "are not within the scope of this guidance." The agencies plan to issue a request for information addressing banks' use of AI, so this is likely to change.
Does NCUA have AI-specific regulations for credit unions?
No. NCUA states it "has not issued AI-specific rules or regulations," and that existing regulations are technology-neutral and apply to AI use. Its supervisory focus is on risk management rather than the tool.
Did NCUA name AI as a 2026 supervisory priority?
No. NCUA's 2026 Supervisory Priorities letter lists balance sheet management, operational risk management, and compliance risk management, with emphasis on BSA/AML. AI is not named in the letter.
What does NCUA expect when a credit union buys AI from a vendor?
NCUA expects the credit union to understand how the product functions, the risks the AI technology introduces, how it fits the business model, and the vendor's safeguards, reliability, and controls. Letters 07-CU-13 and 01-CU-20 set out the third-party due diligence expectations.
Do credit unions need different AI compliance tools than banks?
Often yes, on regulator coverage rather than capability. Many platforms track OCC, Federal Reserve, FDIC, and CFPB content but not NCUA content, a fact that should shape compliance strategies for credit unions.
How do AI compliance tools stay audit-ready under SR 26-2 and FFIEC guidance?
By keeping a complete decision record: inputs, outputs, confidence, reviewer, and any override. SR 26-2 retains the expectation that vendor products be validated, so ask vendors for validation evidence you can hand to an examiner.
Does the EU AI Act affect banks using compliance AI?
For EU operations, yes. AI Act fines reach EUR 35,000,000 or 7% of total worldwide annual turnover, whichever is higher, for prohibited practices under Article 5. Regulation (EU) 2026/1744, in force July 27, 2026, deferred high-risk obligations to December 2, 2027, and August 2, 2028.
How much does AI compliance software cost for a bank or credit union?
Almost all vendors in this category price by quote, scoped to institution size, modules, and volume. Budget for integration, validation, and ongoing governance alongside licensing.
The Rulebook Moved. Your Vendor List Should Too.
The guidance every compliance vendor cites was replaced in April. The framework that most of them claim to align with predates generative AI. NCUA has said in writing that it has no AI rule and no plans to treat AI differently from any other technology. Anyone selling you certainty about the regulatory landscape is selling something the regulators have not written yet.
What has not moved is the underlying expectation. You own the risk, whoever runs the system. Pick tools that show their work, keep human expertise on the decisions that matter, and produce a record you would be comfortable handing to an examiner who has not yet decided what to ask.
Start with one compliance process, automate it end-to-end with full logging, and let the audit trail make the case for the second one.
See Your Compliance Workflow Run Itself
Send us one month of your regulatory change log or your most recent exam findings list. We will run it through AgentFlow and hand back the numbers an examiner would actually read.